The coverage
Ten frameworks.
The ones regulators
and auditors care about.
Policy FastTrack covers the frameworks your auditor will ask about, your customers will demand evidence for, and your regulator already requires. New frameworks (and new requirements within existing ones) are added as they're published.
Best Practice AI Policy
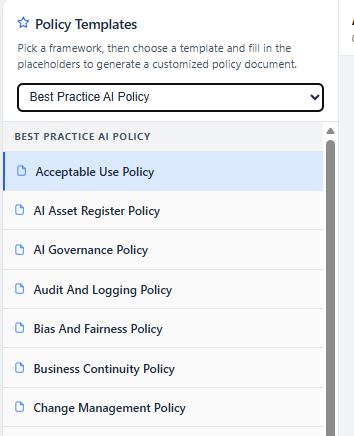
A complete starter set covering the 24 baseline AI policies every organization should have, regardless of which formal framework applies. The foundation most companies start with before layering on framework-specific requirements.
→
ISO/IEC 42001
The international standard for AI management systems. 19 templates covering acceptable use, asset register, impact assessment, risk appetite, supplier policy, ethics oversight, and the rest of the AIMS clause set.
→
NIST AI RMF
The US National Institute of Standards' framework. 16 templates organized into three tiers, from baseline acceptable use through advanced change management and decommissioning policies.
→
SOC 2
The AI controls mapping that bridges your existing SOC 2 program with AI-specific requirements your auditor is starting to ask about.
→
HIPAA
Five templates for healthcare organizations using AI. Patient rights, PHI minimum necessary standard, security risk analysis, breach assessment, and business associate agreements specifically for AI vendors.
→
GDPR
Eight templates for EU compliance. Article 22 automated decision-making, consent management, legal basis assessment, cross-border data transfer, Records of Processing Activities, and the AI-specific Data Protection Impact Assessment.
→
U.S. State AI Laws
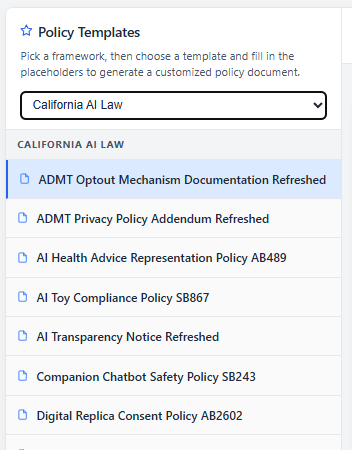
More than 60 templates built on the AI laws states have actually passed, across more than 30 states and New York City: California, Colorado, Connecticut, Illinois, New York, Texas, and more. Disclosure notices, opt-out procedures, bias testing, chatbot safety, and impact assessments. Pair it with the AI Legislation Map to see where all 50 states stand.
→
National AI Laws Worldwide
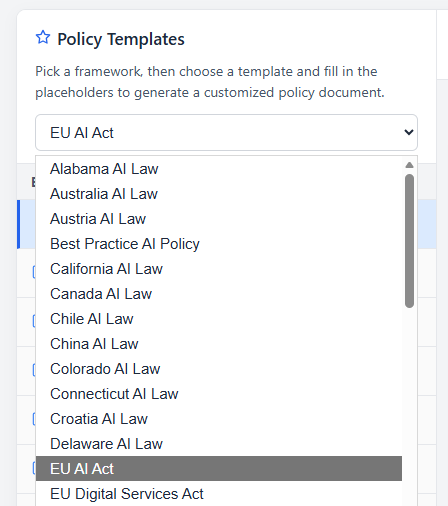
More than 40 templates for national AI and data protection laws around the globe: the EU AI Act and Digital Services Act plus 26 countries, including Canada, Germany, France, Italy, Japan, China, India, Singapore, Australia, Mexico, and Nigeria. Automated decision, transparency, and AI disclosure policies for each.
→
PCI DSS
Two templates for organizations using AI inside their cardholder data environment: scoping/governance policy and targeted risk analysis specifically for AI systems.
→
FedRAMP
Seven templates for federal contractors: AI component disclosure, SSP supplement, federal incident response addendum, CUI handling, transparency and accountability, and FISMA compliance addendum.
→